Gestion des paramètres et de la protection
Commandes disponibles
Pour obtenir une liste de toutes les commandes AdGuard disponibles, sasissez :
adguard-cli --help-all
Activation et désactivation de la protection
Activer la protection
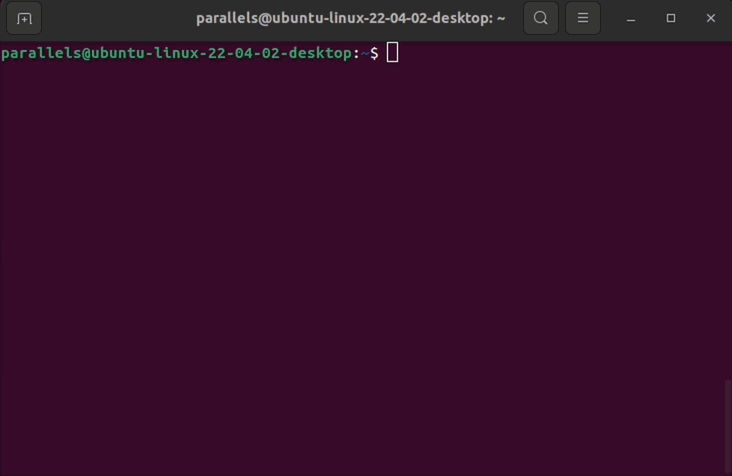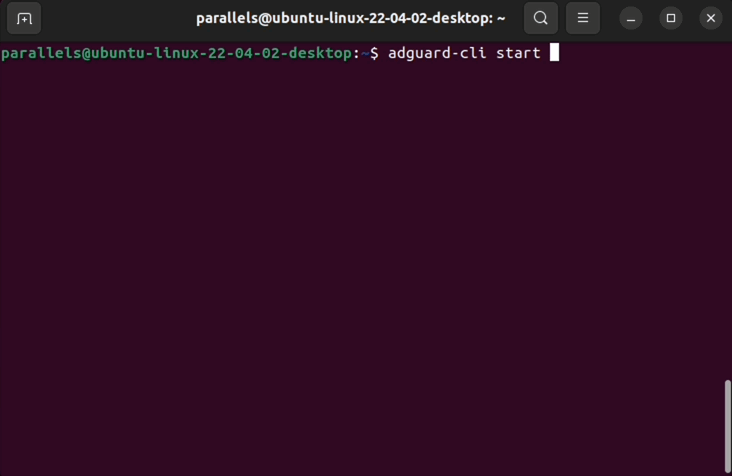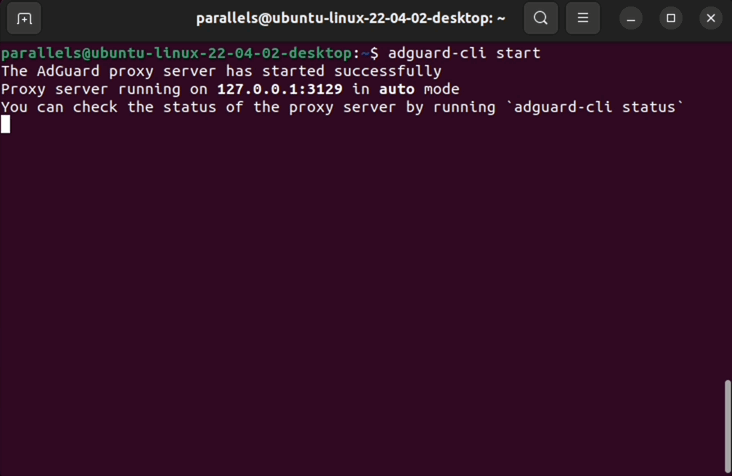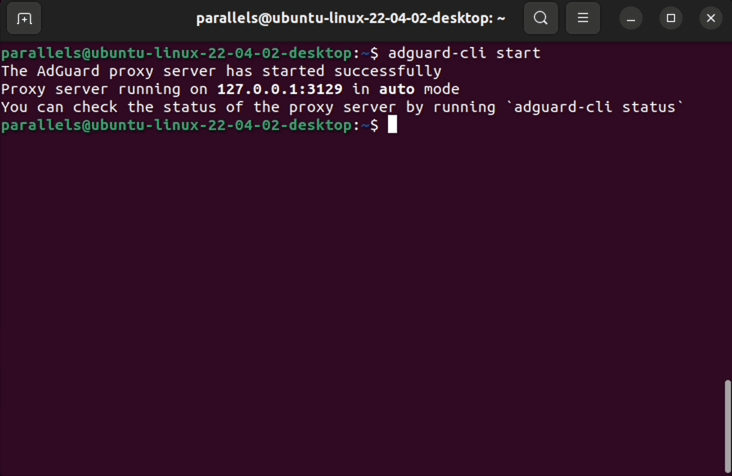
Pour activer la protection, il faut saisir :
adguard-cli start
Cette commande tente de configurer une redirection vers le proxy.
Désactiver la protection
Pour désactiver la protection, saisissez :
adguard-cli stop
This command not only stops the proxy but also stops the traffic from redirecting to it.
Vérifier l'état de protection
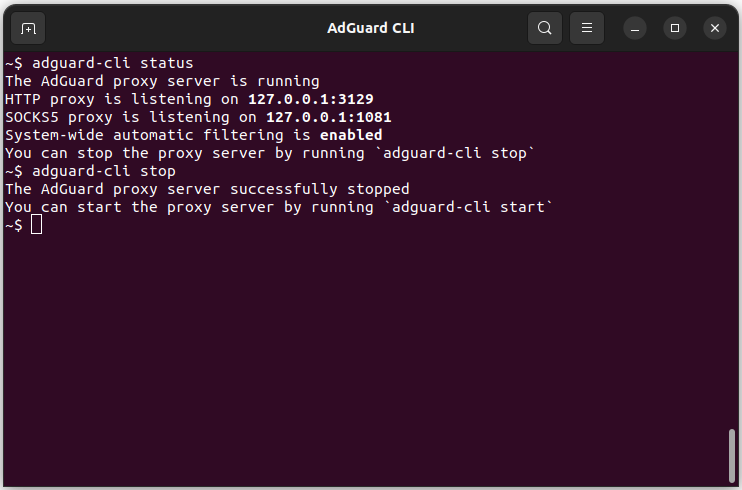
Pour afficher l'état de la protection, il faut saisir :
adguard-cli status
Restart protection
To restart the proxy server and reapply settings, enter:
adguard-cli restart
Updates
Vérification des mises à jour
To check for updates, enter:
adguard-cli check-update
Update AdGuard for Linux
To update AdGuard for Linux, enter:
adguard-cli update
Update script output
To view the update script output, enter:
adguard-cli update -v
Configure AdGuard for Linux
Use the config command to configure AdGuard for Linux. Subcommands:
-
show [<section-name>]: Show the current configuration inproxy.yaml(or a specific section)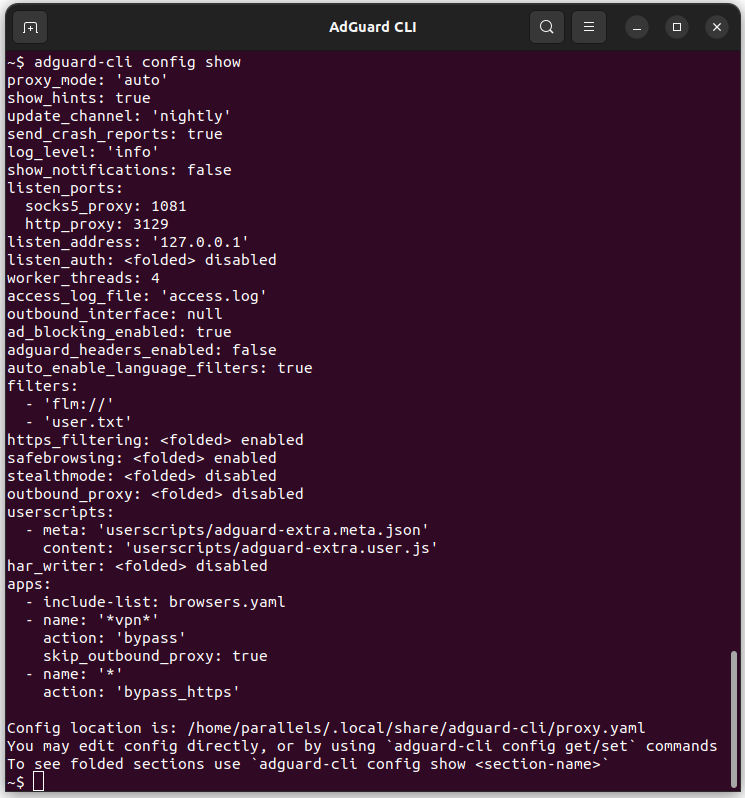
-
set <key> <value>: Configure an option inproxy.yamllisten_ports.http_proxy: HTTP listening portproxy_mode: Proxy mode (manualorauto)
-
get <key>: Get the current status of a setting -
list-add <key> <value> [<value>...]: Add one or more values to a list setting -
list-remove <key> <value>: Remove a value from a list setting -
reset <key>: Reset a setting to its default value -
reset --all: Reset all settings to their default values
The Automatic mode can only be used if the following requirements are met:
iptablesis installed and running (eithernftorlegacy)iptablessupports thenattable for both IPv4 and IPv6iptablessupports theREDIRECTandQUEUEchains for both IPv4 and IPv6- The
sudopackage is installed
Manage filters
Use the filters command to configure AdGuard for Linux. Subcommands:
-
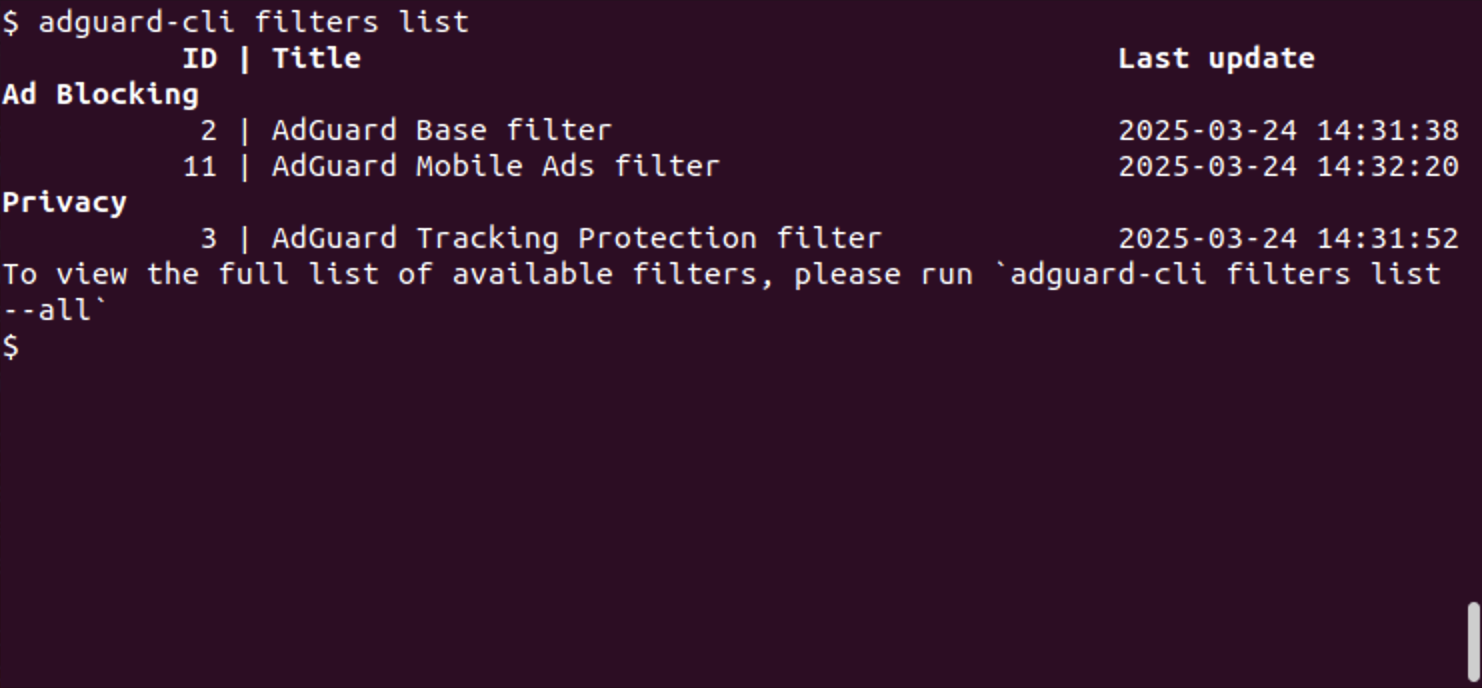
list: List installed and added filters--all: View all filters
-
add: Add a built-in filter by ID or name -
install: Install a filter. Enter the URL of the filter you want to install or local file--trusted: Mark the custom filter as trusted--title: Set a custom title for the filter
-
enable: Enable a filter. Enter the name or ID of the filter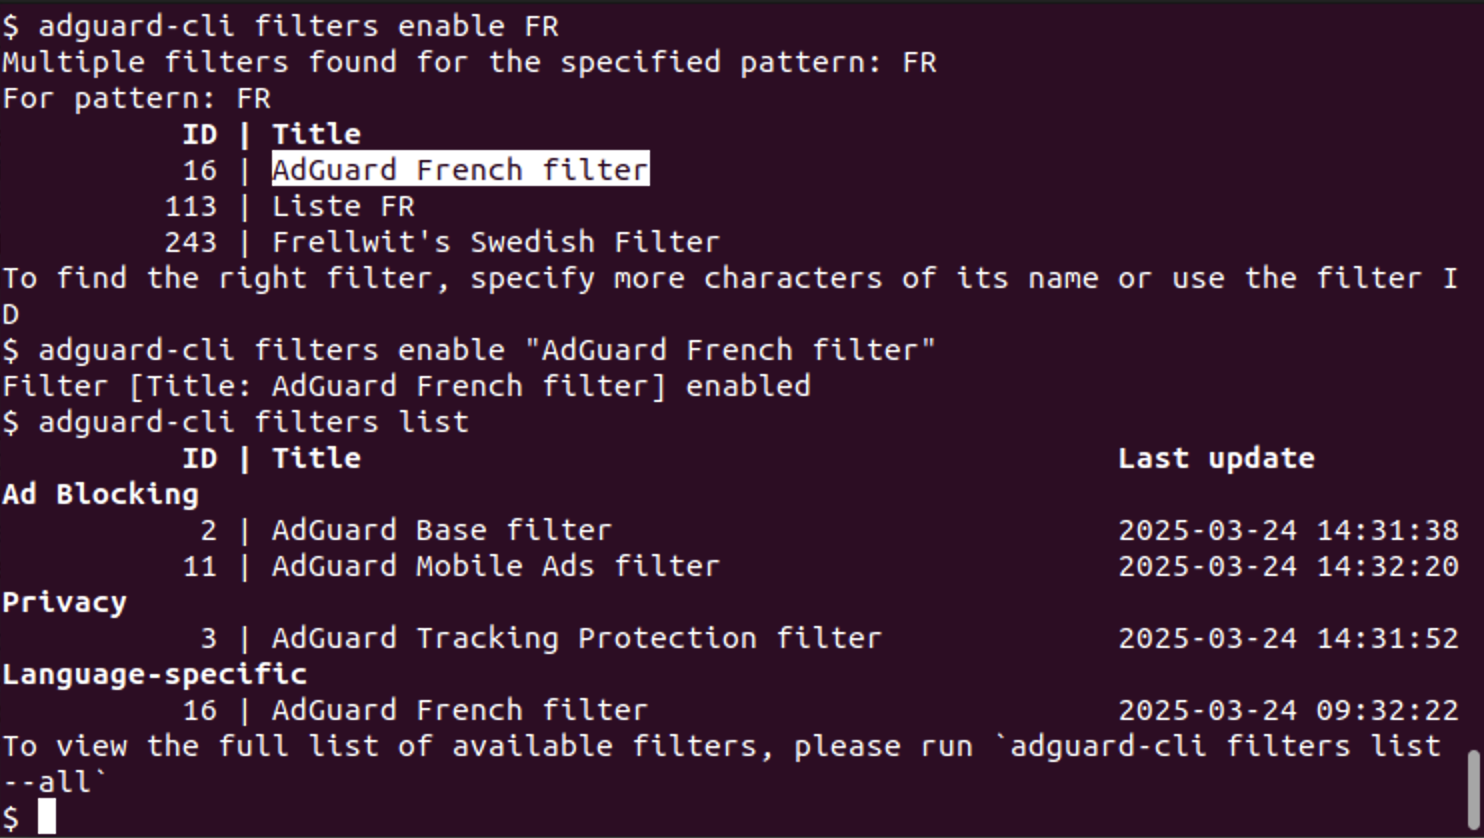
-
disable: Disable a filter. Enter the name or ID of the filter -
remove: Remove an internal or custom filter by ID -
set-trusted: Mark a custom filter as trusted or untrusted -
set-title: Set a custom title for a custom filter
Filter updates are handled by adguard-cli check-update (the filters update subcommand forwards to it).
Manage DNS filters
Use the dns filters command to manage DNS filter lists. Subcommands:
list: List installed and added DNS filters--all: View all DNS filters
add: Add a built-in DNS filter by ID or nameinstall: Install a custom DNS filter from a URL or local file--title: Set a custom title for the filter
enable: Enable a DNS filter. Enter the name or ID of the filterdisable: Disable a DNS filter. Enter the name or ID of the filterremove: Remove a DNS filter by IDset-title: Set a custom title for a DNS filter
DNS filter updates are handled by adguard-cli check-update.
Manage userscripts
Use the userscripts command to manage userscripts. Subcommands:
list: Show installed userscriptsinstall: Install a userscript from a URLremove: Remove a userscriptenable: Enable a userscriptdisable: Disable a userscript
Userscripts are updated by adguard-cli check-update.
Changing the proxy server listen address in manual proxy mode
By default, the proxy server listens on 127.0.0.1 — the address of the loopback network interface.
There are two ways to make the proxy server listen on a different interface:
- Run
adguard-cli config set listen_address <address>where<address>is the address to listen on. - Edit the config file directly:
- To determine the location of the config file, run
adguard-cli config show | grep "Config location". - Look for the
listen_addresskey and set its value accordingly. To listen on all available network interfaces, set the listen address to0.0.0.0or::.
- To determine the location of the config file, run
If the listen address is set to anything other than 127.0.0.1, then proxy client authentication is required. AdGuard CLI will not start unless proxy authentication is configured:
- When running
adguard-cli config set listen_address <address>where<address>is not127.0.0.1, AdGuard CLI will prompt for a username and password if proxy authentication is not already configured. - When editing the config file directly, look for the
listen_authkey. Set theenabledsub-key totrue, andusernameandpasswordto non-empty values.
Configure outbound proxy
You can configure outbound_proxy if you want AdGuard CLI to work through another proxy server.
There are two ways to configure it:
1. Configure via URL (recommended)
Instead of setting each option step by step, you can set all parameters in a single line using a URL:
adguard-cli config set outbound_proxy https://user:pass@host:port
Supported modes are HTTP, HTTPS, SOCKS4, and SOCKS5.
You can also quickly enable or disable outbound_proxy:
adguard-cli config set outbound_proxy false
Or quickly clear the settings:
adguard-cli config set outbound_proxy ""
2. Configure individual parameters
The ability to adjust specific parameters is also available:
adguard-cli config set outbound_proxy.enabled true
adguard-cli config set outbound_proxy.host localhost
adguard-cli config set outbound_proxy.port 3128
adguard-cli config set outbound_proxy.username user
adguard-cli config set outbound_proxy.password pass
Disable certificate verification for HTTPS proxies:
adguard-cli config set outbound_proxy.trust_any_certificate true
Enable SOCKS5 proxy for UDP traffic:
adguard-cli config set outbound_proxy.udp_through_socks5_enabled true
If your SOCKS5 proxy does not support UDP, connections may fail.
Per-app AdGuard CLI configuration
Users often need to enable filtering manually for certain browsers. AdGuard for Linux supports per-app configuration, allowing you to apply settings or rules individually to each application instead of system-wide.
For details, refer to the apps section in proxy.yaml.
A set of pre-configured entries for popular web browsers is included by default in browsers.yaml.
Checking the current configuration
To view the current outbound_proxy configuration, enter:
adguard-cli config show outbound_proxy
Configuring outbound_proxy via URL is available starting from AdGuard for Linux v1.1.26 nightly and v1.1 stable release.
Export and import settings
The export/import functionality allows you to backup your AdGuard CLI configuration and restore it on the same or different system. This includes filters, proxy settings, and other configuration options.
Export settings
To export current AdGuard CLI settings to a ZIP archive, use:
adguard-cli export-settings
You can specify the output path using the -o or --output flag. This can be either a specific file path or a directory:
# Export to a specific file
adguard-cli export-settings -o "/path/to/settings.zip"

# Export to a directory (archive will be created with a standard name)
adguard-cli export-settings -o "/path/to/directory"
If no output path is specified, the settings will be exported to the working directory with a standard name. After successful export, the command will display the full path where the archive was created.
Import settings
To import AdGuard CLI settings from a ZIP archive, use:
adguard-cli import-settings -i "/path/to/settings.zip"
The -i or --input flag is required and specifies the path to the settings archive to import.
Assistant de navigateur AdGuard
L'Assistant de navigateur AdGuard vous permet de gérer la protection AdGuard directement depuis votre navigateur.
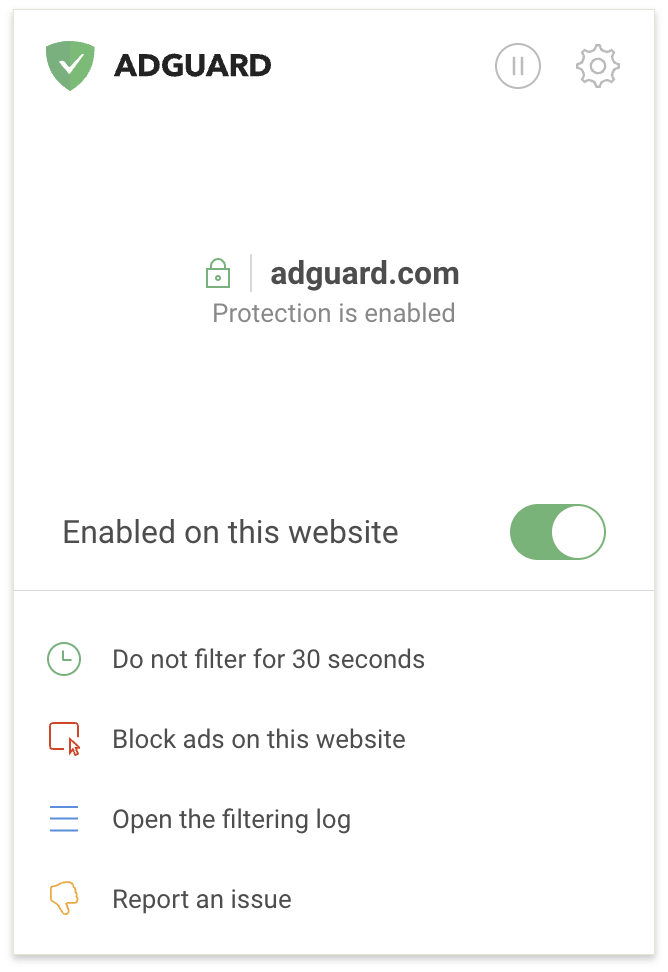
Comment ça marche
L'Assistant AdGuard est une extension de navigateur. It allows you to quickly manage AdGuard for Linux:
- Enable or disable protection for a specific website (the toggle under the website name)
- Interrompez la protection pendant 30 secondes
- Désactivez la protection (l'icône de pause dans le coin supérieur droit)
- Bloquez une annonce manuellement
- Signalez un blocage incorrect
- Manage HTTPS filtering (the lock icon next to the website name)
Comment installer
To install Native Messaging manifests for browser integration, use:
adguard-cli install-browser-integration
To uninstall the manifests, use:
adguard-cli install-browser-integration --uninstall
Install AdGuard Browser Assistant extension:
- Ouvrez la Page de l'Assistant.
- Sous le nom de votre navigateur, sélectionnez Installer.
- Installez l'Assistant à partir de la boutique d'extensions de votre navigateur.
Support for AdGuard Browser Assistant is available starting from AdGuard for Linux v1.4.